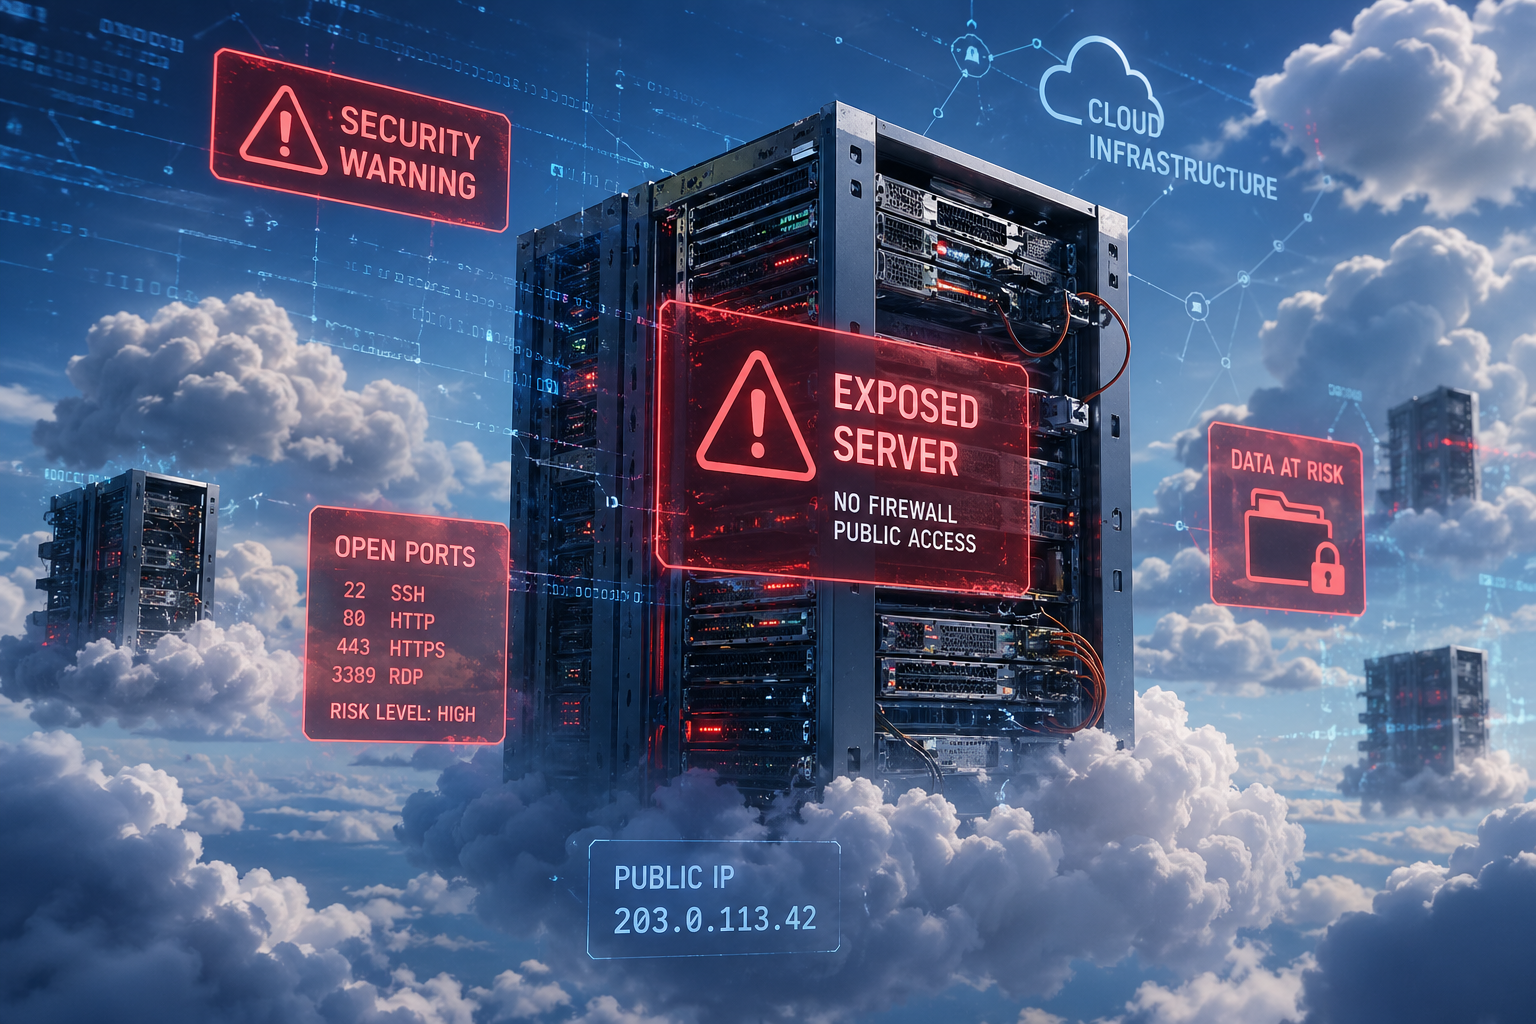
A startup launches its app on the cloud.
Everything is fast. Scalable. Efficient.
They use AWS. Deploy servers. Store user data. Set up permissions.
Within weeks, the app gains users.
Within months…
It gets breached.
Not because AWS was insecure.
But because they made one small mistake.
A single misconfiguration.
What is AWS Security?
AWS provides powerful cloud infrastructure—but security is a shared responsibility.
AWS secures the cloud.
You must secure what’s inside the cloud.
Common AWS Security Mistakes
1. Misconfigured S3 Buckets
Leaving storage publicly accessible
2. Overly Permissive IAM Roles
Giving admin access to everyone
3. No Logging or Monitoring
No visibility into attacks
4. Hardcoded Credentials
Keys exposed in code repositories
5. Lack of Encryption
Sensitive data stored in plain text
Real-World Scenario
A company stores user data in an S3 bucket.
They forget to restrict access.
Anyone with the link can view:
- Emails
- Passwords
- Personal data
Attackers find it using automated tools.
The breach goes viral.
Impact
- Data leaks
- Legal consequences
- Loss of trust
How to Avoid These Mistakes
- Follow least privilege principle
- Enable CloudTrail logging
- Encrypt data
- Use IAM roles carefully
- Regular security audits